Phishing Rises Three Times Faster in Europe Than Globally, Proofpoint Finds
New Proofpoint research reveals phishing detections surged 4.5x across Europe year over year, compared with 1.5x globally
Latest security research news, vulnerabilities, CVEs, and threat intelligence collected periodically from external sources.
New Proofpoint research reveals phishing detections surged 4.5x across Europe year over year, compared with 1.5x globally
Summary Artificial intelligence (AI)-enabled attacks are accelerating, with AI as both a target and a force multiplier. Of the 103 AI-enabled incidents analyzed for this report, most involve AI accelerating familiar attack types (supply-chain compromise, phishing, extortion) and making them more convincing. The use of AI is evident throughout the attack lifecycle, though full automation remains rare. Note: The period of analysis for this report is between July 31, 2025 and July 31, 2026. Developer tools are a prime target. Because AI coding assistants and proxy packages often have privileged …
The tried-and-true recipe for protecting a corporate network has become far less effective than it once was. Guarding the perimeter with a firewall and granting remote access through a VPN gateway has become both cumbersome and risky: day to day, it’s hard to configure how users and cloud services interact, and during cyberattacks the VPN gateway is now a prime target. According to data from insurer At-Bay , nearly three-quarters of the successful ransomware attacks in its 2025 analysis began with a compromised VPN. To jointly improve network security and operational efficiency, companies nee…
Why the Risk Operations Center Is Becoming the System of Record for Proactive Enterprise Risk Reduction The cybersecurity industry has spent years improving how we discover vulnerabilities. The challenge now is no longer finding risk. It is reducing risk faster than adversaries can exploit it. The PHP2Shell vulnerabilities disclosed in October are a reminder of how quickly exposure can become exploitation. Within hours of disclosure, attack activity was already being observed. Across more than 10,000 customer environments, the Qualys Threat Research Unit identified more than 166 million PHP i…
OpenAI on Thursday unveiled GPT‑6 Cyber, which it described as a major step forward in security research that brings together stronger cybersecurity capabilities with a step-change improvement in model alignment. The new model is "more capable at finding and fixing vulnerabilities, and far more reliable staying within the boundaries researchers set," OpenAI said. It has classified the model as
OpenAI GPT-6 Cyber found 81 high-severity Firefox flaws and hundreds of Linux bugs, raising new questions about AI-powered cyber risks. OpenAI has introduced GPT-6 Cyber, a model built for security research that it says finds and fixes vulnerabilities better and stays within the limits researchers set far more reliably. These are OpenAI’s own results and evaluations, so read them as claims to check. “We’re introducing GPT‑6 Cyber, a major leap in security research: more capable at finding and fixing vulnerabilities, and far more reliable staying within the boundaries researchers set. GP…
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research. Called Haiou (meaning Seagull in Chinese), the jailbreak modifies OpenAI Codex's configuration

You run security at your organization. It’s 7:00 am, and you’re having breakfast. You receive a ping: a new critical vulnerability has been disclosed. Your team scrambles to compare vendor advisories, read technical research, check which systems run the affected software, and answer familiar questions from the business: are we affected, and what are we doing about it? Another disclosure arrives before that work is finished. AI is changing both the volume and speed of critical vulnerability discovery. It can analyze large codebases at scale and surface deeply nested flaws that may have existed…
VOLTA is an AI-powered infostealer that steals personal data, then uses LLMs to assess victims’ value and rank targets for attackers. Cisco Talos has analyzed a new Windows infostealer called VOLTA, which calls itself VOLTA-AUTODOXER. It steals the usual data, then hands the loot to a large language model that ranks what the victim is worth. Ryan Fetterman laid it out in a Talos report , after the malware turned up through the CAIRN research effort. “There is a new idea in the cybercrime world — cast a wide net, steal everything, and let AI sort out the specifics. A new malware se…
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between August and October 2026. According to a report published by Dream Research Labs, the campaign has led to the compromise of a high-profile individual in Israel, along with additional compromises affecting a government cloud
Recently, our team exposed sophisticated scam kits designed to steal sensitive data and trick consumers. But underground marketplaces are not just for malware and stolen passwords. They also offer services designed to manipulate your opinion of the products and services you buy every day. In our latest research, we examined cybercrime forums where sellers advertise illicit “reputation management” services. For the right price, these underground operators offer to flood a product with glowing, five-star ratings or remove negative reviews. This shadowy industry works both ways—artificially boos…

Welcome to Kernel Panic, a weekly newsletter by Lily Hay Newman and Matt Burgess from inside the new world of privacy and digital security. To receive this newsletter in your inbox each week, sign up here. New research shared exclusively with Kernel Panic sho…
Yoba malware uses fake ChatGPT and Claude apps to sideload malware through signed installers and deploy a cryptocurrency miner. Check Point Research has spent two months tracking a campaign it calls Yoba, which uses the popularity of AI tools to spread a custom malware chain. The attackers build fake GitHub projects that pose as AI desktop applications such as GPT-5.6 Sol, GPT-6 Astra and Claude Opus. The projects look convincing and run on real GitHub infrastructure, which helps them seem legitimate to potential victims. “These projects look convincing and use real GitHub infrastructur…

Welcome to the 26th edition of Cloudflare's DDoS Threat Report. This edition covers the third quarter of 2026 — July, August, and September — and returns the series to its quarterly cadence following the combined H1 2026 volume. The analysis is produced by Cloudforce One , Cloudflare's Threat Intelligence organization, providing a comprehensive analysis of the evolving threat landscape of Distributed Denial of Service (DDoS) attacks based on data from the Cloudflare network . Key insights Short-burst, low-bandwidth attacks lasting under 10 minutes and 1 Gbps surged by 208%. Converse…
Building your malware analysis lab is a key point before playing with malware. Today, thanks to virtualization, it's convenient to play with snapshots in your lab. Start a new investigation from a clean snapshot and take some more when you reached a critical step. But, if you need to revert to a previous snapshot, all changes applied to the VM are... lost! Therefore, it's important to store important data outside the VM.
Executive Summary Node.js has fixed CVE-2026-111497, a Brotli decoder flaw that can permit remote code execution, in 22.23.4, 24.22.1, and 26.12.1, but upgrading at scale is slow. In Qualys telemetry, only 42,000 of roughly 3 million Node.js installations have been patched, and 1.7 million run end-of-life lines that will never receive a fix. In the meantime, interim mitigations from the Qualys Threat Research Unit narrow the Brotli, DNS, TLS, and keep-alive attack paths, and WAF, IPS, and EDR protections from major vendors add further layers. Soon, Qualys ETM will factor these controls into r…
CVEs: CVE-2026-111497
Research CLI for XSS candidate analysis and local proof labs
Executive Summary On October 21, 2026, Node.js released fixes for 10 vulnerabilities across its three supported release lines: 22.x, 24.x, and 26.x. Four are rated High. The most severe, CVE-2026-111497, is an out-of-bounds write in the bundled Brotli decoder that Node.js says permits remote code execution. These flaws live in the Node.js runtime itself, not in application packages, so application dependency checks will not surface them. Qualys Threat Research Unit data shows that nine in 10 Node.js installations are either unpatched or on lines that will never receive these fixes. Qualys cus…
CVEs: CVE-2026-111497
The Amsterdam-based company plans to use the funding for research and development and commercial expansion in Europe and the Middle East. The post Indurex Raises $8 Million to Expand Industrial Cybersecurity Platform appeared first on SecurityWeek .
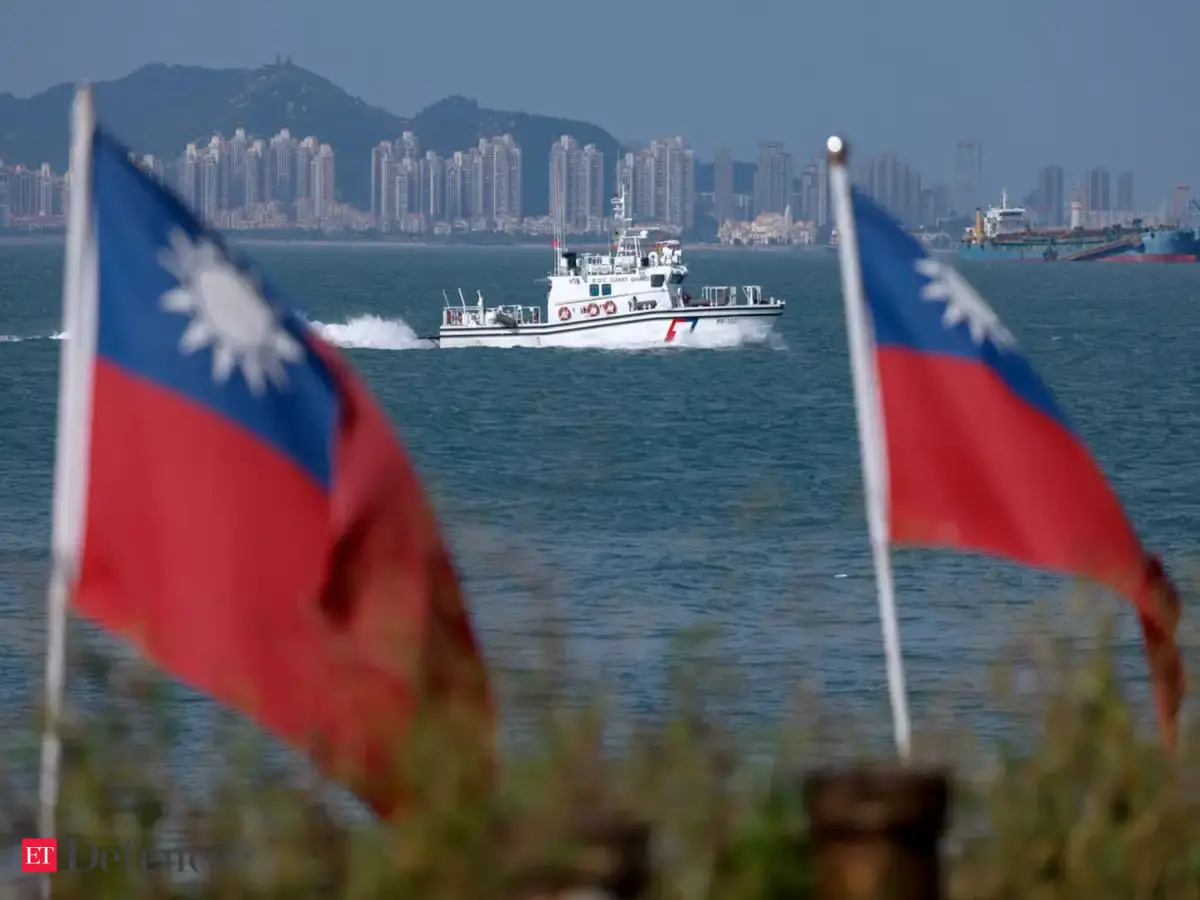
Taiwan's Ministry of National Defence has reported heightened military activity from China around the island recently. Five Chinese military aircraft, six naval vessels, and nine official ships were detected until early Monday. This follows multiple incursion…
Scientific Reports - Comprehensive assessment of historical surface air temperature simulations over iran using 51 CMIP6 models
Scientific Reports - Dynamic association of APLNR with astrocytic remodeling in the cuprizone-treated corpus callosum

A new report finds nearly half of workers are often logging in on Sundays. It is a boon for worker flexibility, or a sign of job-hugging insecurity?

NEW RESOURCES Library of Congress: South Asian Audio: A New Digital Home for the Library’s South Asian Literary Recordings Project (SALRP). “The South Asian Literary Recordings Project (SALRP) has a new home! […]
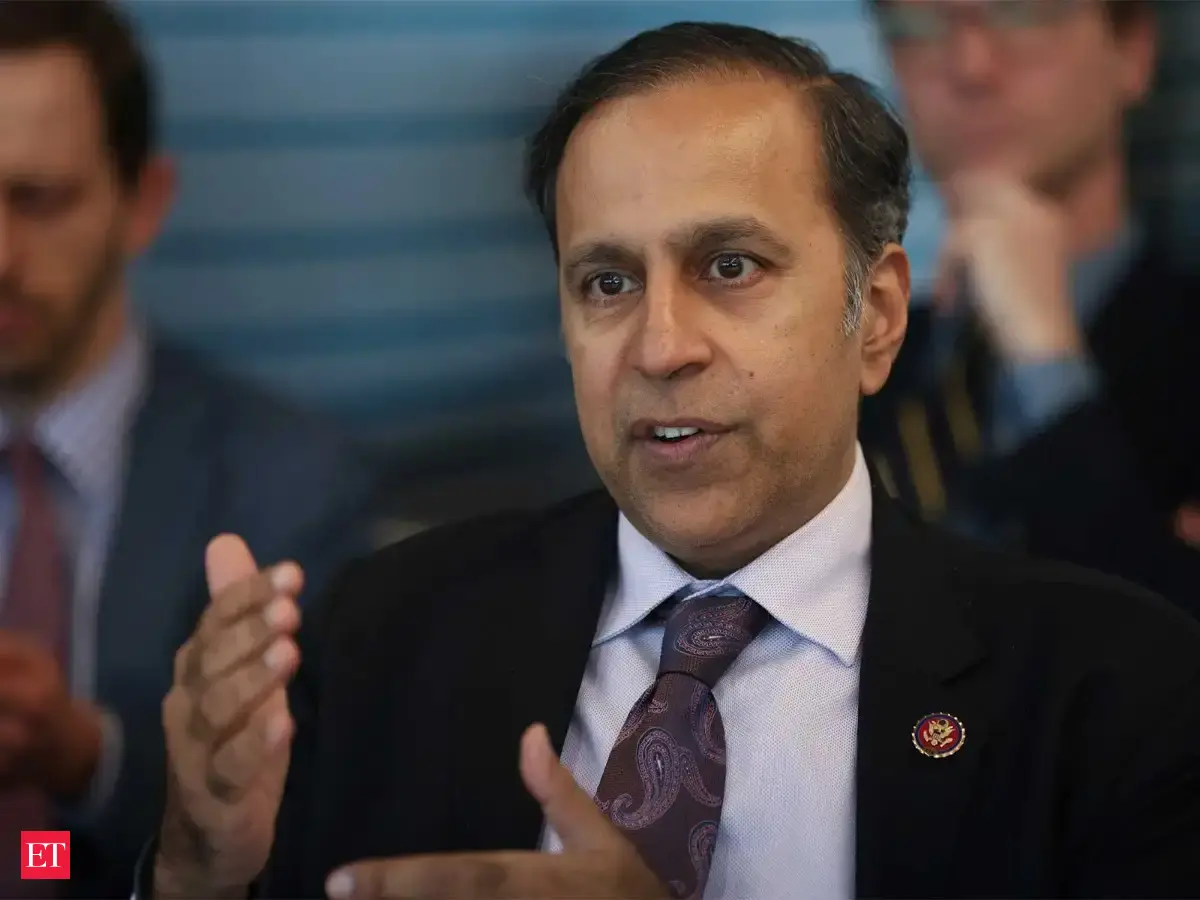
Congressman Raja Krishnamoorthi reported a suspicious package at his Schaumburg district office following similar nationwide mailings. Local emergency responders and federal law enforcement acted quickly to safely remove the package. These incidents involve l…

Somewhere, Nicolas Cage is tipping his cap to the levels of meta ESPN achieved this week. On Thursday, ESPN’s Pete Thamel reported the College Football Playoff “nearing a deal to expand to 24 teams” next season. Subsequently, Thamel reported that ESPN would p…
Group for Apps and Services on Exascale Research Infrastructure is a research, development, and teaching unit at FIDIT + MedRi.
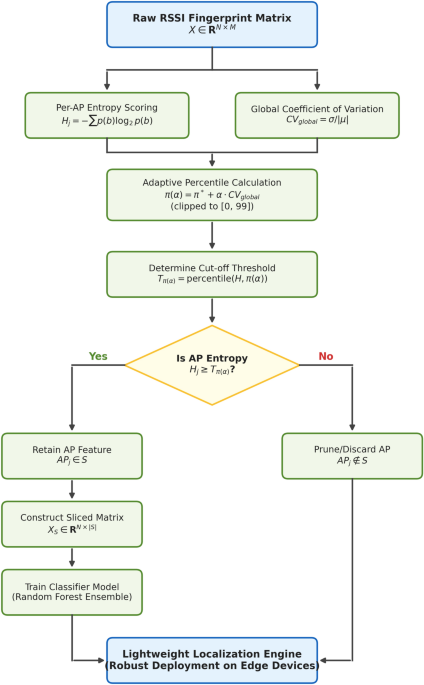
Scientific Reports - Adaptive entropy-guided access point selection for robust multi-floor Wi-Fi fingerprinting
President Donald Trump promised jail for California officials who don’t heed the Department of Justice’s (DOJ) warning that they will be criminally charged if they include the mail-in ballots of the some 200,000 people reportedly identified as potential nonci…

"Cloudflare has acquired Deno, the company behind the [server-side] JavaScript and TypeScript runtime created by Ryan Dahl, the inventor of Node.js," Forbes reported last week. But Deno "has no future at Cloudflare, which will maintain the runtime for anot…